Data processing addendum
Data Processing Addendum
This Data Processing Addendum (“DPA”) supplements the Master Services Agreement, End User License Agreement, Product-Specific Terms, or other written or digital agreement (the “Agreement”) entered into by and Customer and Company. This DPA incorporates the terms of the Agreement, and any capitalized terms that are used but not defined in this DPA shall have the meanings set forth in the Agreement.
1. Definitions
1.1 “Authorized Subprocessor” means a third-party entity engaged by Company to process Personal Data in order to provide the Services and that has been approved by Customer in accordance with Section 6.
1.2 “Company Account Data” means personal data that relates to Company’s relationship with Customer, including the names or contact information of individuals authorized by Customer to access Customer’s account and billing information of individuals that Customer has associated with its account.
1.3 “Company Usage Data” means Service usage data collected and processed by Company in connection with the provision of the Services, including without limitation data used to identify the source and destination of a communication, activity logs, and similar data.
1.4 “Data Subject” means a natural person whose Personal Data is protected by Privacy Laws. For the avoidance of doubt, “Data Subject” includes the term “Consumer” under Privacy Laws.
1.5 “Data Subject Request” means a request from a Data Subject to exercise their rights over Personal Data afforded pursuant to Privacy Laws.
1.6 “EU SCCs” means standard contractual clauses approved by the European Commission in Commission Decision 2021/914 dated 4 June 2021, for transfers of personal data to countries not otherwise recognized as offering an adequate level of protection for personal data by the European Commission (as amended and updated from time to time), as modified by Section 9 of this DPA.
1.7 “ex-EEA Transfer” means the transfer of Personal Data subject to the GDPR from the European Economic Area (the “EEA”), to a country where the transfer is not governed by an adequacy decision made by the European Commission in accordance with the relevant provisions of the GDPR.
1.8 “ex-UK Transfer” means the transfer of Personal Data subject to Chapter V of the UK GDPR from outside the United Kingdom (the “UK”) where such transfer is not governed by an adequacy decision made by the Secretary of State in accordance with the relevant provisions of the UK GDPR and the Data Protection Act 2018.
1.9 “Personal Data” means any information provided to Company by or on behalf of Customer in connection with the Services that relates to an identified or identifiable Data Subject and constitutes “personal data,” “personal information,” or equivalent term under Privacy Laws.
1.10 “Privacy Laws” means any applicable laws and regulations in any relevant jurisdiction relating to the processing of Personal Data including, each to the extent applicable: (i) the General Data Protection Regulation (Regulation (EU) 2016/679) (“EU GDPR”) and the EU GDPR as it forms part of the law of England and Wales by virtue of section 3 of the European Union (Withdrawal) Act 2018 (the “UK GDPR”) (together, collectively, the “GDPR”), (ii) the Swiss Federal Act on Data Protection, (iii) the UK Data Protection Act 2018, (iv) the Privacy and Electronic Communications (EC Directive) Regulations 2003, (v) U.S. state comprehensive privacy laws, such as the California Consumer Privacy Act, as amended by the California Privacy Rights Act of 2020 (the “CCPA”), and (vi) applicable federal, state, and local laws and regulations governing employee and personnel monitoring, workplace surveillance, and electronic communications in the employment context, including without limitation laws requiring notice to or consent from employees or contractors regarding the monitoring, interception, or collection of electronic communications, screen activity, network traffic, device usage, access credentials, or other system activity data; in each case, to the extent applicable to Company’s processing of Personal Data on behalf of Customer and as updated, amended or replaced from time to time. The terms “affiliates,” “business purpose,” “Controller,” “Processor,” “process” or “processing,” “sell,” “share,” or “supervisory authority,” shall have the meanings set forth for those or equivalent terms under Privacy Laws. For the avoidance of doubt, the terms “Controller” and “Processor” include “Business” and “Service Provider,” respectively, as defined in the CCPA.
1.11 “Standard Contractual Clauses” means, as applicable, the EU SCCs and the UK SCCs.
1.12 “UK Addendum” means the template International Data Transfer Addendum issued by the Information Commissioner and laid before Parliament in accordance with s119A of the Data Protection Act 2018 on 2 February 2022 (as may be amended from time to time), as completed by Exhibit D. “UK SCCs” means the EU SCCs, as amended by the UK Addendum.
2. Role of the Parties; Description of Processing
2.1 Except as expressly set forth in this DPA or the Agreement, with respect to Personal Data, Customer is the Controller and Company is a Processor, or to the extent Customer is a Processor to a third-party Controller, Company is a subprocessor.
2.2 Company shall process Personal Data only (i) for purposes set forth in the Agreement, (ii) in a manner consistent with the documented instructions provided by Customer, which shall include the Agreement and this DPA, and (iii) as required by Privacy Laws or a supervisory authority; in such case, Company shall inform Customer of that legal requirement before processing to the extent legally permitted. The subject matter, nature, purpose, and duration of this processing, as well as the types of Personal Data collected and categories of Data Subjects involved, are described in Exhibit A to this DPA.
3. Customer’s Obligations
3.1 Customer shall, in its use of the Services, at all times process Personal Data, and provide instructions for the processing of Personal Data, in compliance with Privacy Laws. Customer shall ensure that the processing of Personal Data in accordance with Customer’s instructions will not cause Company to be in breach of the Privacy Laws. Customer is solely responsible for the accuracy, quality, and legality of (i) the Personal Data provided to Company by or on behalf of Customer, (ii) the means by which Customer acquired any such Personal Data, and (iii) the instructions it provides to Company regarding the processing of such Personal Data. Without limiting the foregoing, prior to making any Personal Data available to Company or deploying the Services in a manner that involves the processing of Personal Data, Customer shall provide all notices to, and obtain all consents, authorizations, or acknowledgments from, employees, contractors, and other Data Subjects, in each case as required under Privacy Laws, including without limitation any notices or consents required under applicable employee monitoring, workplace surveillance, and electronic communications laws. Customer shall not provide or make available to Company any Personal Data in violation of the Agreement or otherwise inappropriate for the nature of the Services, and shall indemnify and hold harmless Company from all claims, losses, damages, costs, and expenses (including reasonable attorneys’ fees) in connection therewith. Company shall immediately notify Customer if an instruction, in Company’s opinion, infringes Privacy Laws or instruction of a supervisory authority.
4. Use of Personal Data
4.1 Company shall not: (i) sell or share Personal Data; (ii) retain, use, or disclose Personal Data outside of Company’s direct business relationship with Customer or for any purpose other for a business purpose under the CCPA on behalf of Customer or than as necessary to perform the Services for Customer pursuant to the Agreement, except as otherwise permitted in Agreement or by Privacy Laws; and (iii) combine Personal Data received from, or on behalf of, Customer with Personal Data that it receives from, or on behalf of, another party or person, except as necessary to provide the Services or as otherwise instructed by Customer.
5. Audit
5.1 Company shall maintain records sufficient to demonstrate its compliance with its obligations under this DPA. Upon Customer’s written request, but no more than once per twelve (12) month period absent a documented security incident, and subject to reasonable confidentiality controls and reasonable advance notice of at least thirty (30) days, Company shall make available for Customer’s review copies of records demonstrating Company’s compliance with prevailing data security standards applicable to the processing of Personal Data. If Customer and Company have entered into Standard Contractual Clauses as described in Section 9 (Transfers of Personal Data), the parties agree that the audits described in Clause 8.9 of the EU SCCs shall be carried out in accordance with this Section 1.
5.2 To the extent permitted under Privacy Laws, if Customer determines that Company is processing Personal Data in an unauthorized manner, Customer may, taking into account nature of Company’s processing and the nature of the Personal Data processed by Company on behalf of Customer, and upon providing prior written notice, take commercially reasonable and appropriate steps to stop and remediate such unauthorized processing as set forth in this DPA.
6. Authorized Subprocessors
6.1 Customer acknowledges and agrees that Company may (1) engage its affiliates as well as the Authorized Subprocessors listed at https://sidekicksecurity.ai/subprocessors, which is incorporated by reference, or, if no such resource is designated, in Section 4 of Exhibit B to this DPA, to access and process Personal Data in connection with the Services (the “List”) and (2) from time to time engage additional third parties for the purpose of providing the Services, including without limitation the processing of Personal Data pursuant to Section 6.2. Any such linked resource is incorporated into this DPA by reference, and in the event of a conflict between the linked resource and Exhibit B, the linked resource shall control. By way of this DPA, Customer provides general written authorization to Company to engage subprocessors as necessary to perform the Services.
6.2 Customer acknowledges that Company may update the List from time to time, Company has provided a mechanism for Customer to receive notifications of new Authorized Subprocessors by sending an opt-in request to subprocessors@sidekicksecurity.ai to be added to Company’s subprocessor notification distribution list, and Customer agrees to opt in to such notifications by such means. At least ten (10) days before enabling any third party other than existing Authorized Subprocessors to access or participate in the processing of Personal Data, Company will add such third party to the List and notify Customer, which notice may be given by email to the addresses subscribed to such distribution list. Customer may object to such an engagement by informing Company within ten (10) days of receipt of the aforementioned notice to Customer, provided such objection is in writing and based on reasonable, specific data protection grounds. Company will evaluate such objection in good faith. If Customer does not object during this period, that third party will be deemed an Authorized Subprocessor.
6.3 Customer acknowledges that certain subprocessors are essential to providing the Services and that objecting to the use of a subprocessor may prevent Company from offering the Services to Customer. If Customer reasonably objects to an engagement in accordance with Section 6.2, and Company cannot provide a commercially reasonable alternative within a reasonable period of time, Customer may discontinue the use of the affected Service by providing written notice to Company. Discontinuation shall not relieve Customer of any fees owed to Company under the Agreement.
6.4 Company will enter into a written agreement with the Authorized Subprocessor imposing on the Authorized Subprocessor data protection obligations comparable to those imposed on Company under this DPA with respect to the protection of Personal Data. In case an Authorized Subprocessor fails to fulfill its data protection obligations under such written agreement with Company, Company will remain liable to Customer for the performance of the Authorized Subprocessor’s obligations under such agreement.
6.5 If Customer and Company have entered into Standard Contractual Clauses as described in Section 9 (Transfers of Personal Data), (i) the above authorizations will constitute Customer’s prior written consent to the subcontracting by Company of the processing of Personal Data if such consent is required under the Standard Contractual Clauses, and (ii) the parties agree that the copies of the agreements with Authorized Subprocessors that must be provided by Company to Customer pursuant to Clause 9(c) of the EU SCCs may have commercial information, or information unrelated to the Standard Contractual Clauses or their equivalent, removed by Company beforehand, and that such copies will be provided by Company only upon request by Customer.
7. Confidentiality; Security of Personal Data
7.1 Company shall ensure that any person it authorizes to process Personal Data has agreed to protect Personal Data in accordance with Company’s confidentiality obligations in the Agreement. Customer agrees that Company may disclose Personal Data to its advisers, auditors or other third parties as reasonably required in connection with the performance of its obligations under this DPA, the Agreement, or the provision of Services to Customer.
7.2 Taking into account the state of the art, the costs of implementation and the nature, scope, context and purposes of processing as well as the risk of varying likelihood and severity for the rights and freedoms of natural persons, Company shall maintain appropriate technical and organizational measures to ensure a level of security appropriate to the risk of processing Personal Data, as described in Exhibit C.
8. Personal Data Breach
8.1 In the event of a Personal Data Breach, Company shall, without undue delay, inform Customer of the Personal Data Breach and take such steps as Company in its sole discretion deems necessary and reasonable to remediate such Personal Data Breach, to the extent that remediation is within Company’s reasonable control.
8.2 In the event of a Personal Data Breach, Company shall, taking into account the nature of the processing and the information available to Company, provide Customer with reasonable cooperation and assistance necessary for Customer to comply with its obligations under Privacy Laws.
8.3 The obligations described in Sections 8.1 and 8.2 shall not apply in the event that a Personal Data Breach results from the actions or omissions of Customer. Company’s obligation to report or respond to a Personal Data Breach under Sections 8.1 and 8.2 will not be construed as an acknowledgement by Company of any fault or liability with respect to the Personal Data Breach.
9. Transfers of Personal Data
9.1 The parties agree that Company may transfer Personal Data processed under this DPA outside the EEA, the UK, or Switzerland as necessary to provide the Services. Customer acknowledges that Company’s primary processing operations take place in the United States, and that the transfer of Personal Data to the United States is necessary for the provision of the Services to Customer. If Company transfers Personal Data protected under this DPA to a jurisdiction for which the European Commission has not issued an adequacy decision, Company will ensure that appropriate safeguards have been implemented for the transfer of Personal Data in accordance with Privacy Laws.
9.2 Ex-EEA Transfers. The Parties agree that ex-EEA Transfers shall either be made pursuant to the EU SCCs, which are deemed entered into (and incorporated herein by reference) and completed as follows:
9.2.1 Module One (Controller to Controller) of the EU SCCs applies when Company is processing Personal Data as a controller pursuant to Section 9 of this DPA.
9.2.2 Module Two (Controller to Processor) of the EU SCCs applies when Customer is a controller and Company is a processor of Personal Data in accordance with Section 2 of this DPA.
9.2.3 Module Three (Processor to Subprocessor) of the EU SCCs applies when Customer is a processor and Company is a subprocessor of Personal Data in accordance with Section 2 of this DPA.
9.2.4 For each module, where applicable the following applies:
9.2.5 The optional docking clause in Clause 7 does not apply.
9.2.6 In Clause 9, Option 1 (general written authorization) applies, and the minimum time period for prior notice of subprocessor changes shall be as set forth in Section 6.1 of this DPA.
9.2.7 In Clause 11, the optional language does not apply.
9.2.8 All square brackets in Clause 13 are hereby removed.
9.2.9 In Clause 17 (Option 1), the EU SCCs will be governed by the laws of the Republic of Ireland.
9.2.10 In Clause 18(b), disputes will be resolved before the courts of the Republic of Ireland.
9.2.11 Exhibit B to this DPA contains the information required in Annex I of the EU SCCs.
9.2.12 Exhibit C to this DPA contains the information required in Annex II of the EU SCCs.
9.2.13 By entering into this DPA, the Parties are deemed to have signed the EU SCCs incorporated herein, including their Annexes.
9.4 Ex-UK Transfers. The Parties agree that ex-UK Transfers shall either be made pursuant to (i) the Data Privacy Framework to the extent that recipient of the ex-UK Transfer is certified accordingly, or (ii) the UK SCCs, which are deemed entered into and incorporated herein by reference. The UK Addendum (including the EU SCCs incorporated into it) is (1) governed by the laws of England and Wales and (2) any dispute arising from it is resolved by the courts of England and Wales.
9.5 Transfers from Switzerland. The Parties agree that transfers from Switzerland shall either be made pursuant to (i) the Data Privacy Framework to the extent that recipient of the transfer from Switzerland is certified accordingly, or (ii) the EU SCCs with the following modifications:
9.5.1 The terms “General Data Protection Regulation” or “Regulation (EU) 2016/679” as utilized in the EU SCCs shall be interpreted to include the Federal Act on Data Protection of 19 June 1992 (the “FADP,” and as revised as of 25 September 2020, the “Revised FADP”) with respect to data transfers subject to the FADP.
9.5.2 Clause 13 of the EU SCCs is modified to provide that the Federal Data Protection and Information Commissioner (“FDPIC”) of Switzerland shall have authority over data transfers governed by the FADP and the appropriate EU supervisory authority shall have authority over data transfers governed by the GDPR. Subject to the foregoing, all other requirements of Clause 13 shall be observed.
9.5.3 The term “EU Member State” as utilized in the EU SCCs shall not be interpreted in such a way as to exclude Data Subjects in Switzerland from exercising their rights in their place of habitual residence in accordance with Clause 18(c) of the EU SCCs.
9.6 Supplementary Measures. In respect of any transfer of Personal data made pursuant to the Standard Contractual Clauses, the following supplementary measures shall apply:
9.6.1 As of the date of this DPA, Company has not received any formal legal requests from any government intelligence or security service/agencies in the country to which the Personal Data is being exported, for access to (or for copies of) such Personal Data (“Government Agency Requests”).
9.6.2 If Company receives a Government Agency Request, Company shall attempt to redirect the government agency to Customer. As part of this effort, Company may provide Customer’s basic contact information to the government agency. If Company is compelled to disclose Personal Data, to the extent legally permitted, Company shall notify Customer of the demand and reasonably cooperate to allow Customer to seek a protective order or other appropriate remedy. Company shall not voluntarily disclose Personal Data to any law enforcement or government agency. The Parties shall determine whether all or any transfers of Personal Data pursuant to this DPA should be suspended in the light such a Government Agency Request.
9.6.3 The Parties will confer as appropriate to consider whether: (i) the protection afforded by the laws of the country of Company to data subjects whose Personal Data is being transferred is sufficient to provide broadly equivalent protection to that afforded in the EEA or the UK, as applicable; (ii) additional measures are reasonably necessary for the transfer to comply with Privacy Laws; and (iii) it is still appropriate for Personal Data to be transferred to the relevant Company, taking into account all relevant information available, including guidance by supervisory authorities, to the Parties.
9.6.4 If either (i) any of the means of legitimizing a transfer cease to be valid or (ii) any supervisory authority requires transfers of Personal Data pursuant to those means to be suspended, the Parties agree to amend the means of legitimizing transfers in accordance with Privacy Laws. To the extent necessary to ensure the enforceability of the Standard Contractual Clauses, the Parties shall execute the Standard Contractual Clauses as a separate agreement.
10. Data Protection Assessments
10.1 Taking into account the nature of Company’s processing and the information available to Company, Company shall reasonably cooperate with Customer to conduct any data protection or privacy impact assessments as required by Privacy Laws. Notwithstanding the foregoing, Customer and Company each remain responsible only for the measures respectively allocated to them under Privacy Laws pertaining to any such assessment.
11. Data Subject Request
11.1 Company shall, to the extent permitted by Privacy Laws, notify Customer within a reasonable time upon receipt of a Data Subject Request. If Company receives a Data Subject Request in relation to Personal Data, Company will advise the Data Subject to submit their request to Customer and Customer will be responsible for responding to such request. Customer is solely responsible for ensuring that Data Subject Requests communicated to Company are valid, and, if applicable, for ensuring that a record of consent to processing is maintained with respect to each Data Subject.
12. Return or Destruction of Personal Data
12.1 Upon the termination or expiration of the Agreement, and subject to Customer’s written request within thirty (30) days of such termination or expiration, Company shall return or delete Personal Data, unless further storage of such Personal Data is required or authorized by applicable law or Company’s standard data retention policies. In the absence of such written request, Company may delete Personal Data in accordance with its standard practices. If Customer and Company have entered into Standard Contractual Clauses as described in Section 9 (Transfers of Personal Data), the parties agree that the certification of deletion of Personal Data that is described in Clause 8.1(d) and Clause 8.5 of the EU SCCs (as applicable) shall be provided by Company to Customer only upon Customer’s written request.
13. Company’s Role as a Controller
13.1 The parties acknowledge and agree that with respect to Company Account Data and Company Usage Data, Company is an independent controller, not a joint controller with Customer. Company will process Company Account Data and Company Usage Data as a controller (i) to manage the relationship with Customer; (ii) to carry out Company’s core business operations, such as accounting, audits, tax preparation and filing and compliance purposes; (iii) to monitor, investigate, prevent and detect fraud, security incidents and other misuse of the Services, and to prevent harm to Customer; (iv) for identity verification purposes; (v) to comply with legal or regulatory obligations applicable to the processing and retention of Personal Data to which Company is subject; and (vi) as otherwise permitted under Privacy Laws and in accordance with this DPA and the Agreement. Company may also process Company Usage Data as a controller to provide, optimize, and maintain the Services, to the extent permitted by Privacy Laws. Any processing by Company as a controller shall be in accordance with Company’s privacy policy.
14. Miscellaneous
14.1 In the event of any conflict or inconsistency among the following documents, the order of precedence will be: (1) the applicable terms in the Standard Contractual Clauses; (2) the terms of this DPA; (3) the Agreement, and (4) Company’s privacy policy. Any claims brought in connection with this DPA will be subject to the terms of the Agreement, including, but not limited to, the exclusions and limitations set forth in the Agreement.
Exhibit A — Details of Processing
Nature and Purpose of Processing: Company will process Personal Data as necessary to provide the Services under the Agreement, for the purposes specified in the Agreement and this DPA, and in accordance with Customer’s instructions as set forth in this DPA. The nature of processing includes, without limitation, processing of Personal Data for security and fraud prevention purposes, including monitoring and analyzing system usage patterns to detect unauthorized access or anomalous behavior, authenticating users and verifying access credentials, detecting, investigating, and preventing fraudulent or malicious activity, and monitoring system integrity.
Duration of Processing: Company will process Personal Data as long as required (i) to provide the Services to Customer under the Agreement; (ii) for Company’s legitimate business needs; or (iii) by applicable law or regulation. Company Account Data and Company Usage Data will be processed and stored as set forth in Company’s privacy policy.
Categories of Data Subjects: The Personal Data made available to Company is determined and controlled by the Customer, in its sole discretion, while configuring the Services. Categories of data subject may include customer end-users, customers, and/or employees.
Categories of Personal Data: Company processes Personal Data contained in Company Account Data, Company Usage Data, and any Personal Data provided by Customer. The Company also processes the following categories of Personal Data: (i) Customer personnel/employee system usage data; (ii) IP addresses; (iii) authentication data; and (iv) fraud signals. The Personal Data made available to Company is determined and controlled by the Customer, in its sole discretion, while configuring the Services.
Sensitive Data or Special Categories of Data: The Personal Data made available to Company is determined and controlled by the Customer, in its sole discretion, while configuring the Services.
Exhibit B — Standard Contractual Clauses Information
1. The Parties
The following includes the information required by Annex I and Annex III of the EU SCCs, and Table 1, Annex 1A, and Annex 1B of the UK Addendum.
The Parties:
Data exporter(s):
Name: Customer;
Address: As designated in the Agreement;
Contact person’s name, position and contact details: As designated in the Agreement;
Signature and date: By entering into the DPA, Customer is deemed to have signed these Standard Contractual Clauses incorporated herein;
Role (controller/processor): As provided in Section 2 of this DPA.
Data importer(s):
Name: Company;
Address: As designated in the Agreement;
Contact person’s name, position and contact details: As designated in the Agreement;
Signature and date: By entering into the DPA, Company is deemed to have signed these Standard Contractual Clauses incorporated herein;
Role (controller/processor): As provided in Section 2 of this DPA.
2. Description of Transfer

3. Competent Supervisory Authority
The supervisory authority shall be the supervisory authority of the Data Exporter, as determined in accordance with Clause 13 of the EU SCCs. The supervisory authority for the purposes of the UK Addendum shall be the UK Information Commissioner’s Office.
4. List of Authorized Subprocessors
The current List of Authorized Subprocessors is available at https://sidekicksecurity.ai/subprocessors, which is incorporated herein by reference.
Exhibit C — Technical and Organisational Security Measures
Description of the Technical and Organisational Security Measures implemented by the Data Importer. The information required by Annex II of the EU SCCs and Appendix II of the UK Addendum is set forth in Company’s description of its technical and organizational security measures available at https://sidekicksecurity.ai/security, which is incorporated into this Exhibit C and this DPA by reference.
Exhibit D — UK Addendum
UK Addendum. International Data Transfer Addendum to the EU Commission Standard Contractual Clauses. Part 1: Tables.
Table 1: Parties

Table 2: Selected SCCs, Modules and Selected Clauses

Table 3: Appendix Information
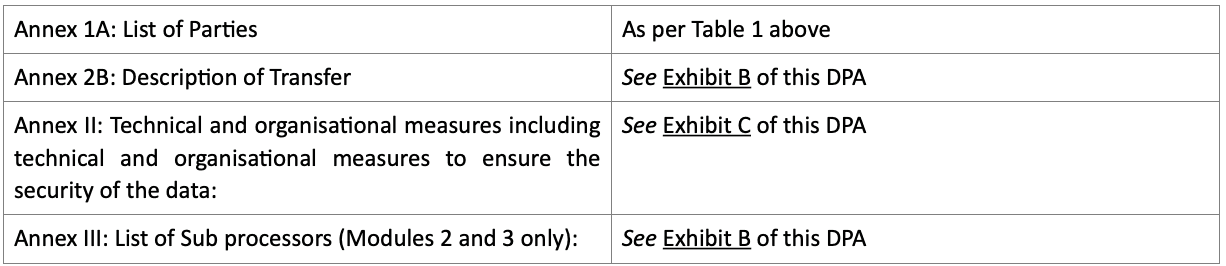
Table 4: Ending this UK Addendum when the Approved UK Addendum Changes

Part 2: Mandatory Clauses.
The Mandatory Clauses of the UK Addendum are incorporated herein by reference.